 strange.rand
Reality check
Posted the idea of this project on Reddit and received valuable (negative) feedback.
My motivation for moving matching to the server was:
- More control: threshold, number of images per finger, auto-update of fingerprints (as smartphones do).
- The decision is made not in the exposed region (reader).
- Easier to manage (clean hierarchy: person -> finger -> templates) and better control over enrollment.
The biggest downsides are:
- The blast radius. With matching on a chip, a hacked server means someone can open your door. With matching on the server, it may lead to stolen fingerprint images or templates.
- Fingerprints are non-revocable. A stolen fingerprint is forever.
Here I need to note that probably all hobby-grade fingerprint sensors are vulnerable and may leak your fingerprints, as communication over unencrypted UART means anyone can send any command, including a template export or get a raw image. Despite the reconstruction of the original fingerprint image from the template being impossible (AFAIK), it is possible to construct a synthetic image that will pass the lock using that template.
Changing the concept
As of now, the idea is to support multiple authentication methods:
- NFC using a smartphone (Android only)
- NFC using a card (DESFire, NTAG 424)
- Fingerprint
- PIN
The current phase is NFC using a smartphone, and it already works on the bench. The private key lives in the phone’s secure hardware and never leaves it. The server stores only the public key. Enrollment is done once (hardware attestation + manual approval). On every tap, the server sends a signed one-time challenge, the phone verifies it and signs it back. A recorded exchange can’t be replayed, and a leaked database has nothing to steal.
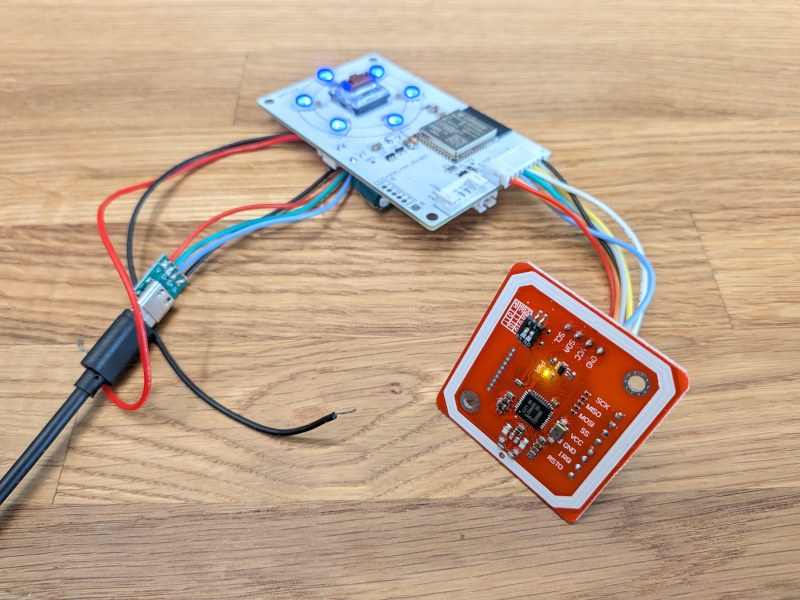
I'm renaming the project to Kindly Identify Yourself (KIY). Naming a project is almost as hard as naming variables, and in this field, almost every good word is already taken. So I went to the Culture series by Iain M. Banks to find something interesting.
What about a fingerprint reader?
As of now, it is still planned, and I'm waiting for the sensors. I'll do what I can to reduce the risks (e.g., raw images won't be stored, and templates will be encrypted), and of course it'll be an optional method (probably with the possibility of disabling it during installation).
Discussions
Become a Hackaday.io Member
Create an account to leave a comment. Already have an account? Log In.